Compliance and risk
Push the AML, sanctions and conduct update to every employee before the rule takes effect.

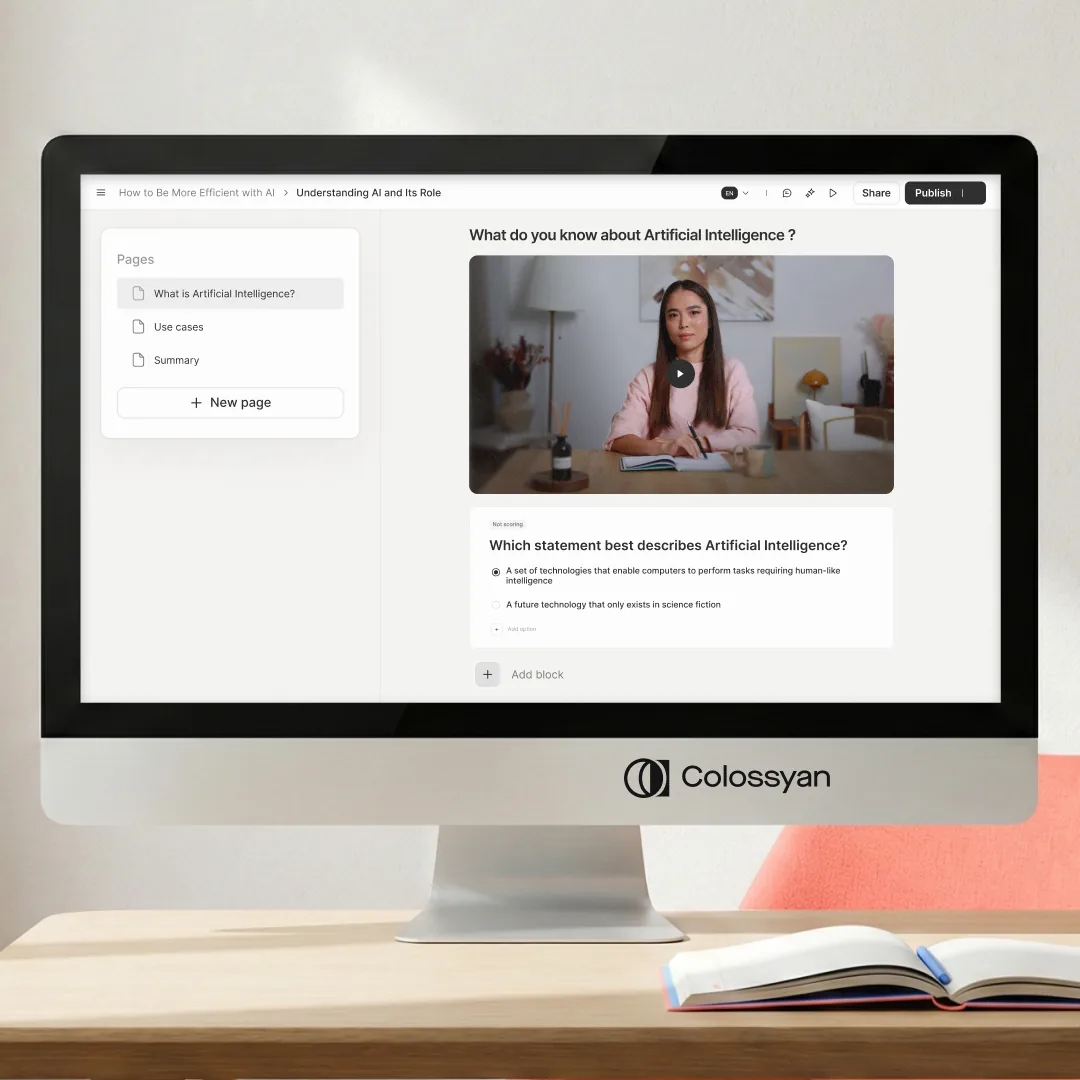
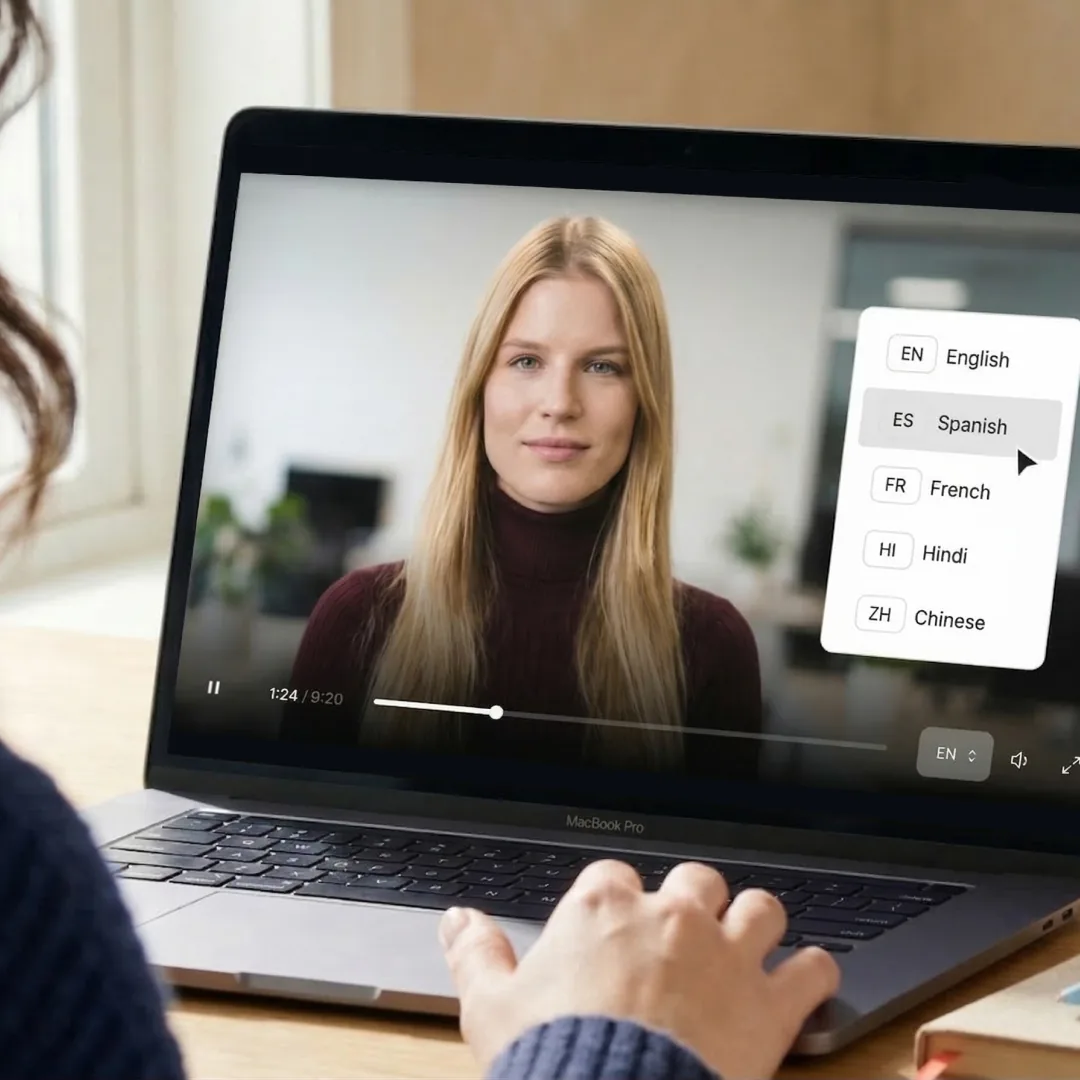
Turn the policies you already have into courses and video training your people finish and your examiners can verify. Edit one lesson, republish the same day, in every language your branches speak.
Trusted by regulated teams at
A rule changes in March and the course gets rebuilt in the next annual cycle.
Nearly two thirds of compliance, risk and HR teams say a vendor course edit takes a week or longer.
Compliance Week and Ethena, 2025. 134 professionals surveyed.
42% name evolving requirements as their biggest compliance roadblock.
2025 financial services compliance report.
Enterprises localise 73% of their learning content on average.
Survey of 300+ L&D professionals.
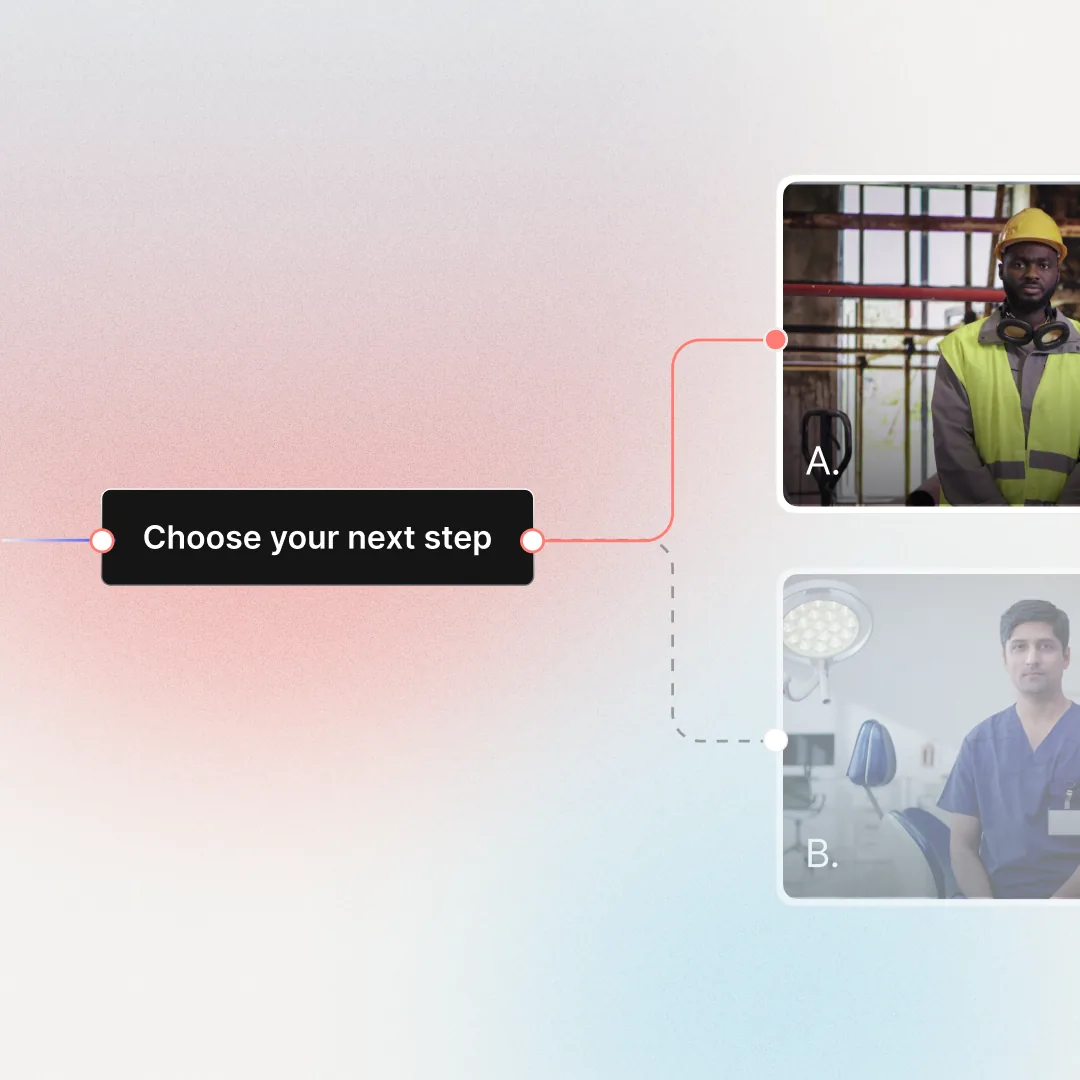
A new client wants their savings in one hot stock. Your advisor picks a response and sees where each choice leads, so suitability is practiced before a real client is in the chair.
Off-the-shelf courses cover the regulation. Not your products, your states or last week's rate change.
Ongoing, risk based
No fixed federal interval. Annual in practice, plus training after a material change.
Source: FinCEN, 31 CFR 1020.210, FFIEC
Every calendar year
Due 31 December. Next year's topics published by 1 October.
Source: FINRA Rule 1240(a)
Annual written plan
Driven by the firm's own needs analysis. No fixed number of hours.
Source: FINRA Rule 1240(b)
Commonly 24 hrs per 2 yrs
Usually including 3 ethics hours. Varies by state.
Source: state insurance departments
At least annually
Periodic under the Compliance Commitments Framework. Changes can bite immediately.
Source: OFAC Framework
Before the effective date
No fixed cycle. Examiners expect training updated in advance of a rule taking effect.
Source: CFPB and OCC guidance
"There's no way that we're gonna find anything off the shelf."
Compliance, the branch network and the advisors all work from the same library, so one rule change updates every course.
Push the AML, sanctions and conduct update to every employee before the rule takes effect.
New products, KYC checks and service scripts in short modules.
Brief advisors on suitability, disclosures and new products.
Mandatory regulatory training in a new hire’s first week.
Ship the process change as a 90 second video, not a memo.
The biggest benefit of Colossyan is being able to have training material that never goes obsolete.

Instead of sending a boring email, I create a quick avatar message and distribute it. People love it.

Before Colossyan, creating a short video took around 4 hours. Now it is only an hour, and updating it is much easier.
Colossyan is SOC 2 Type II certified and GDPR compliant, with SSO/SAML, role-based access control, and workspace-level permissions. Your content is not used to train our AI models.
Security, availability, and confidentiality controls, audited.
Data handled to EU data-protection standards.
Authenticate through Okta, Entra ID, or Google Workspace.
Custom roles and permissions at the workspace level.
Your uploaded content, scripts, courses and videos stay yours.
Separate spaces per team or initiative, access controlled.
Colossyan feeds your courses into your existing LMS through SCORM. We add to your stack, we do not replace your system of record.
Financial services compliance training is the recurring employee training that banks, credit unions, broker-dealers, insurers and wealth managers must deliver to meet regulatory obligations. Core topics are BSA and AML, sanctions and OFAC screening, KYC, consumer protection including UDAAP and fair lending, data safeguarding under GLBA, and product and suitability knowledge. FINRA registered people also complete the Regulatory Element every calendar year.
It depends on the rule, and most do not say annual. FINRA's Regulatory Element is the clearest case: every calendar year, due 31 December. BSA and AML rules require ongoing, risk based training with no fixed federal interval, although annual delivery is common practice. OFAC's Compliance Commitments Framework says periodic training at least annually. CFPB and OCC examination guidance expects training to be updated in advance of a new rule's effective date rather than at the next annual cycle.
Examiners look at five things: a written programme, a designated compliance officer, internal controls, independent testing, and training. Training is the pillar that most often shows up as a finding, because it is the easiest to let go stale and the hardest to evidence after the fact.
Yes. Regulators care about the content, the delivery and the record, not how the video was produced. Colossyan courses and videos export as SCORM packages into the LMS you already run, which records each learner's completion and score. You write the script from your own approved policy text, and nothing is generated or published until your team has checked it.
The same day. Edit the affected lesson or scene, save it as a new version and republish. There is no reshoot, no vendor quote and no production queue, and every language version regenerates from the same script. For context, nearly two thirds of compliance, risk and HR professionals say a vendor course edit takes a week or longer (Compliance Week and Ethena, 2025).
No, and that is deliberate. Colossyan is the platform for building and maintaining your own training, not an off-the-shelf course library. In 2025 FINRA sanctioned firms for using vendor supplied generic red flags that were never tailored to their own business. Your policies, your products and your red flags make better training and stand up better in an exam.
Colossyan is SOC 2 Type II certified and GDPR compliant, with SAML single sign-on, role based access control and workspace level permissions. Your uploaded content, scripts, courses and videos are not used to train our AI models. Full security documentation is available through the Trust Center on request.
Yes. Colossyan exports courses as SCORM packages into the system of record you already run, including Cornerstone, Docebo, Moodle and TalentLMS. It adds to your stack rather than replacing it, so completion history and audit reporting stay where your examiners expect them. See all integrations.
Bring a policy PDF to the call. We will turn it into a training course while you watch, and map Colossyan to your security review, your LMS and your examiners.
 PowerPoint
 PDF
 Word
 Articulate
 EasyGenerator
 Elucidat
 360Learning
 Cornerstone
 Docebo
 Moodle
 TalentLMS
 SAP Litmos
 SCORM
 Zapier
 YouTube
 Embed
 Share Link